SITREP: Mumbai Mira Road Stabbing Case, Red Fort Attack Pattern and Emerging Lone-Wolf Radicalisation Indicators
Attack Pattern: Religious Targeting and Identity Verification
Investigations indicate that the attacker engaged the victims in a religious exchange prior to the assault, reportedly asking them about their faith and instructing them to recite the Kalma. Upon non-compliance, he proceeded to stab them. This sequence suggests that the attack was not random but involved identity-based targeting, aligning with behavioural markers observed in ideologically driven lone-actor attacks where coercion precedes violence. Such patterns are often associated with attempts to assert ideological dominance at the point of execution, thereby elevating the incident from a simple assault to a potentially motivated act of violence rooted in extremist narratives.
Radicalisation Indicators: ISIS Influence and Digital Footprint
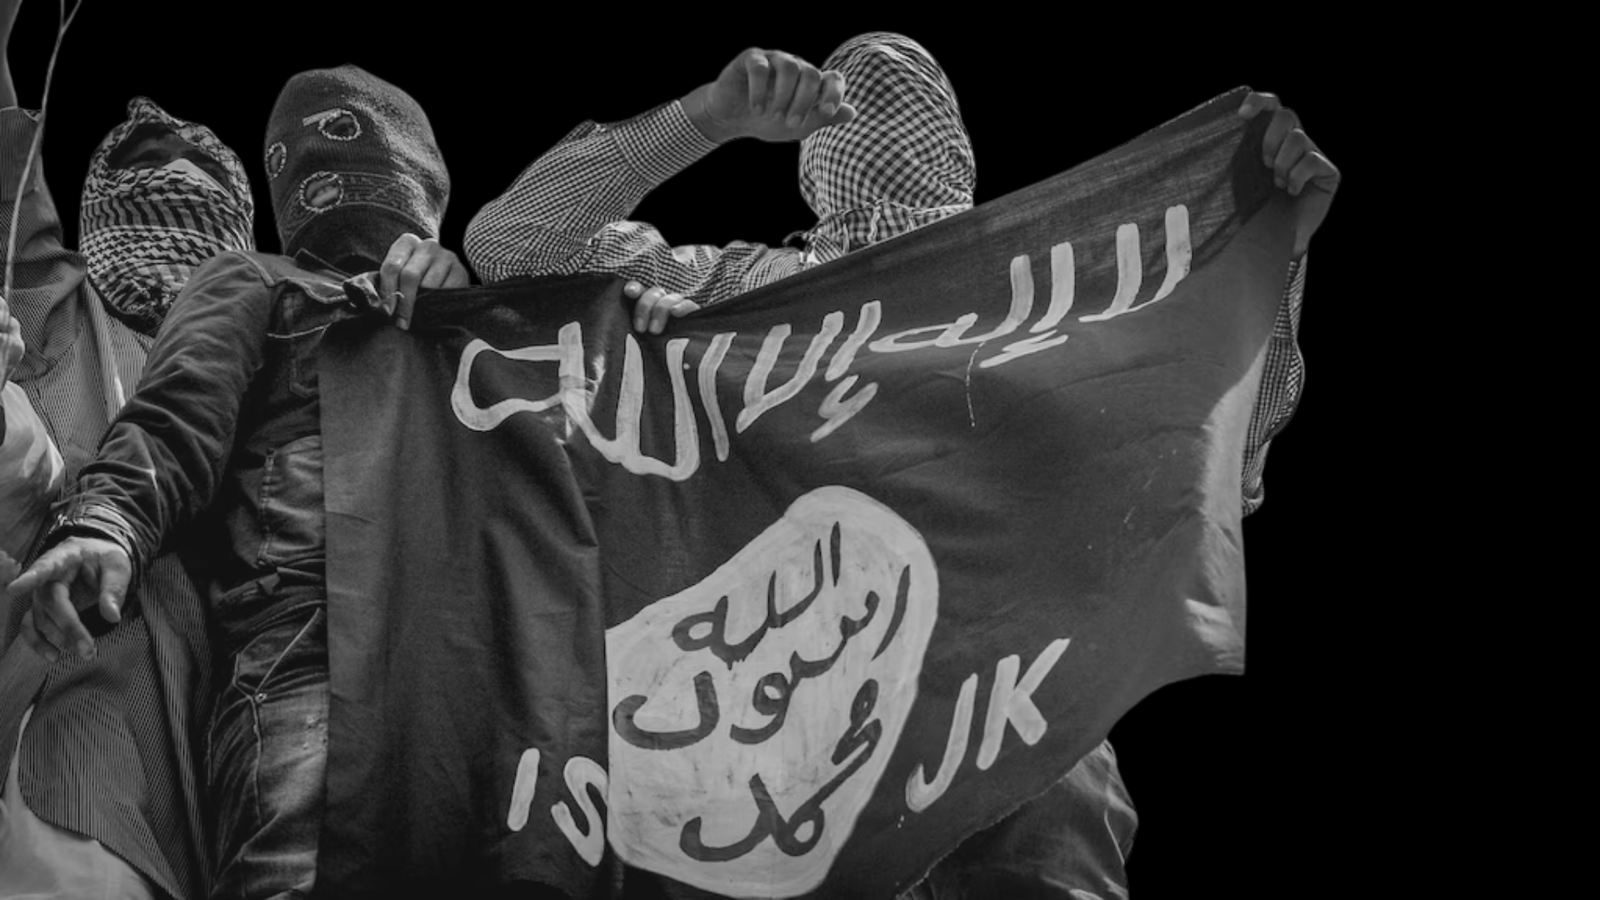
Subsequent searches and digital analysis have revealed concerning radicalisation indicators. Authorities reportedly recovered notes and materials referencing terms such as “lone wolf,” “ISIS,” and “jihad,” alongside evidence suggesting sustained consumption of extremist propaganda. These findings point toward a trajectory of self-radicalisation, likely driven by exposure to online ecosystems rather than direct physical contact with organised groups. The presence of such material indicates that the individual may have transitioned from passive ideological consumption to cognitive internalisation and eventual violent action, a pathway increasingly observed in contemporary terrorism trends.
Investigation Status: Lone Wolf or Network Link?
The case is currently being investigated by the Maharashtra Anti-Terrorism Squad, with preliminary assessments suggesting a “lone wolf” style attack carried out by a self-radicalised individual. However, key uncertainties remain under examination, including whether there were any external handlers, facilitators, or indirect influence networks involved. At present, the incident appears to be operationally executed by a single individual, but with a strong likelihood of ideological connectivity to broader transnational jihadist narratives, rather than direct organisational control.
Intelligence Indicators: Threat Assessment and Confidence Levels
From an intelligence standpoint, several indicators can be classified with varying degrees of confidence. At a high confidence level, the attack appears premeditated, featuring an ideological trigger and a deliberate identity-verification step prior to violence, along with the recovery of extremist-linked material. At a moderate level of confidence, the radicalisation pathway appears consistent with ISIS-inspired lone-actor models, though without confirmed organisational linkage. At a lower confidence level, aspects such as direct connections to any terror organisation or evidence of external facilitation remain unverified and subject to ongoing investigation.
Analytical Assessment: Lone Actor with Ideological Alignment
The most plausible assessment at this stage is that of a self-radicalised lone actor influenced by global jihadist propaganda, executing a low-complexity but symbolically significant attack. Alternative possibilities include the incident representing an early-stage “signal attack” intended to demonstrate intent or attract recognition from transnational groups, or a hybrid case involving online radicalisation combined with personal or local grievance triggers. Regardless of the exact pathway, the operational simplicity of the attack underscores its replicability.
Tactical Overlap: Similarities with Pahalgam Attack Modus Operandi
Strategically, the incident reinforces the persistence of low-cost, high-impact threats within India’s internal security environment, particularly targeting soft and unprotected individuals such as security guards. The attack required minimal planning, no sophisticated logistics, and no evident network support, thereby lowering traditional detection thresholds and complicating pre-emption efforts. The behavioural pattern observed, especially the use of religious identity verification prior to violence, mirrors tactics seen in previous ideologically motivated attacks, including similarities with the modus operandi observed during the Pahalgam incident, where victims were identified and segregated based on religious markers before being targeted. This overlap is significant. It suggests not just coincidence, but the possible diffusion of a tested tactical template within extremist ecosystems, where identity verification acts as both a psychological tool and an operational filter. Such methods amplify fear, create symbolic messaging, and reinforce ideological narratives during execution. The replication of this pattern in a geographically and operationally distinct setting like Mumbai indicates that even decentralised or self-radicalised actors may be drawing from a shared pool of tactics, either through digital propagation or prior case awareness. This strengthens the assessment that while actors may be isolated, the playbook is increasingly standardised, raising the risk of similar incidents being emulated elsewhere with minimal barriers to execution.
Radicalisation of Educated Individuals: Emerging Pattern
Another notable dimension of the case is the socio-educational profile of the accused, which mirrors patterns observed in Red Fort blast in India. Zaib Zubair Ansari is reported to have been educated in the United States and was working as a tutor in Mumbai, teaching subjects such as science and mathematics. This profile of being educated, globally exposed, and professionally engaged aligns with Red Fort Blast where individuals involved in extremist activities were not socio-economically marginal but instead possessed technical or academic backgrounds, including professionals such as doctors.
This profile aligns with the perpetrarors of Red Fort blast. This similarity is analytically significant as it challenges the conventional assumption that extremism is primarily driven by deprivation or lack of opportunity. Instead, it reinforces the emerging pattern of cognitive radicalisation among educated individuals, often facilitated by online ecosystems and ideological echo chambers rather than physical networks. In such cases, education does not act as a barrier but can sometimes enhance the individual’s ability to internalise, rationalise and operationalise extremist narratives. The Mira Road incident, when viewed alongside earlier cases, suggests that the threat landscape is increasingly characterised by high-agency individuals who are self-motivated, ideologically driven, and capable of independent action, thereby complicating detection and prevention frameworks.
Strategic Implications: Shift Toward Decentralised Terrorism
This incident should be understood as part of a broader shift in the threat landscape, where terrorism is increasingly characterised by decentralised, self-activated individuals rather than structured organisations. Digital ecosystems are emerging as key radicalisation incubators, enabling individuals to transition from ideological exposure to violent action without direct organisational involvement. The primary concern lies not in the scale of the attack but in its potential for replication.
Bottom Line: Small Incident, High Strategic Signal
While the incident remains limited in scale, it carries significant strategic implications. It represents a credible case of ideology-driven violence with strong indicators of self-radicalisation and possible alignment with transnational extremist narratives. Although direct attribution to any specific organisation remains unconfirmed, the evolving pattern suggests an early-stage lone actor threat that warrants sustained monitoring and deeper investigation.